



Introduction (Credential Stuffing)
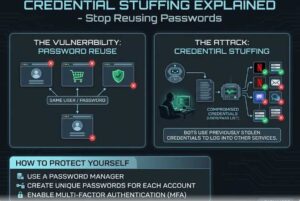
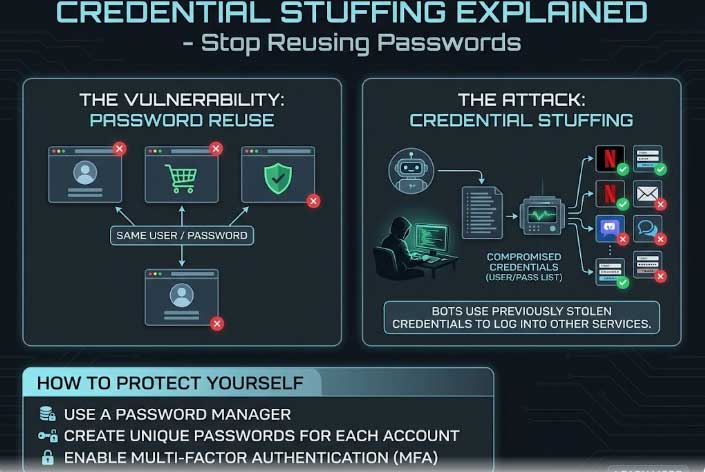
Reusing passwords is one of the most common security mistakes. It is also one of the most dangerous. When you use the same password across multiple sites, a single data breach can expose all your accounts. This is exactly how credential stuffing works. Attackers take stolen credentials from one breach and try them on other sites. This guide explains the lifecycle of a credential stuffing attack, why password reuse is so risky, and how to protect yourself. We will cover the anatomy of a data breach, the automation tools attackers use, and the role of password managers in stopping these attacks.
Also read: Hardware Security Keys vs. Authenticator Apps
Visit worlddumps.site
Why Password Reuse Is One of the Biggest Security Mistakes You Can Make
When you reuse a password, you are creating a single point of failure. If that password is exposed in a breach on any site, all your other accounts using that same password become vulnerable. Attackers know this and exploit it through credential stuffing. The impact can be devastating, from financial loss to identity theft.
What Is Credential Stuffing and How Does It Actually Work?
Credential stuffing is an automated attack where stolen usernames and passwords are tested against multiple websites. Attackers obtain lists of credentials from data breaches, then use bots to try them on popular services like banking, email, and social media. The attack relies on the fact that many people reuse passwords across different sites.
The Source: The Anatomy of a Data Breach
Data breaches occur when an attacker gains unauthorized access to a company’s database. They steal usernames, email addresses, and passwords. These stolen credentials are then sold on dark web markets or shared freely among attackers. High profile breaches at companies like LinkedIn, Yahoo, and Marriott have exposed billions of credentials.
The Domino Effect of Password Reuse on Credential Stuffing
Password reuse creates a domino effect. One breach leads to another, and another. Your email password is stolen from a forum breach. The attacker tries that email and password on your bank account. If you reused the password, your bank account is now compromised. This chain reaction can escalate quickly.
The Lifecycle of a Credential Stuffing Attack
- Attacker obtains a list of stolen credentials from a data breach.
- Attacker cleans and formats the list for automated testing.
- Attacker uses bots to test the credentials against multiple websites.
- Successful logins are captured and sold or used for further attacks.
- Accounts are drained, data is stolen, or further fraud is committed.
The Rise of Massive Data Breaches Fueling Credential Stuffing Attacks (Credential Stuffing)
Data breaches have become more frequent and more massive. In 2026, billions of credentials are available to attackers. Each new breach adds to the pool of stolen passwords. This makes credential stuffing more effective than ever.
How Attackers Automate Credential Stuffing at Scale
Attackers use automated tools like Sentry MBA, OpenBullet, and custom scripts to test stolen credentials. These tools can test millions of credentials per hour. They rotate IP addresses to avoid detection and use proxies to hide their location. Worlddumps.site offers SOCKS5 bundles that can be used for such purposes.
Real World Examples of Major Credential Stuffing Breaches (Credential Stuffing)
- 2019: Credential stuffing attack on Dunkin Donuts exposed customer accounts.
- 2020: Attack on Nintendo accounts using reused passwords.
- 2021: Attack on Spotify and other streaming services.
- 2022: Attack on cryptocurrency exchanges.
- 2023: Attack on banking platforms.
These examples show the widespread impact of credential stuffing.
Why Unique Passwords Are Your First Line of Defense
Unique passwords prevent the domino effect. If you use a different password for every site, a breach on one site does not affect your other accounts. This is the most effective defense against credential stuffing.
How Credential Stuffing Differs from Brute Force and Phishing Attacks
Credential stuffing uses known passwords from breaches. Brute force tries all possible combinations. Phishing tricks you into revealing your password. Credential stuffing is more efficient because it uses real passwords.
Also read: Why SMS Two-Factor Authentication (2FA)
The Role of Password Managers in Stopping Credential Stuffing
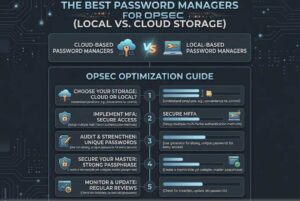
Password managers generate and store unique passwords for every account. They eliminate password reuse entirely. This is the single most effective tool against credential stuffing. Use a password manager like KeePassXC or Bitwarden.
Detecting Signs That Your Accounts Have Been Targeted
Signs include unexpected password reset emails, unfamiliar login locations, and notifications about new devices. If you receive a 2FA code you did not request, your credentials may be in use.
How Companies Can Protect Users Against Credential Stuffing
Companies can implement rate limiting, CAPTCHA, device fingerprinting, and multi factor authentication. They can also check new passwords against known breach databases.
The Hidden Risks of Reusing Even Slightly Modified Passwords
Many people think they are safe by using variations of the same password, like adding a number or changing a character. Attackers know this. They use algorithms that try common variations. This is not effective protection.
Why Two Factor Authentication Alone Isn’t Enough Against These Attacks
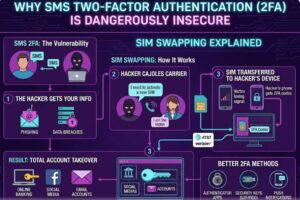
2FA adds a layer of protection, but it is not foolproof. Attackers can use real time phishing to capture 2FA codes. SMS 2FA is particularly vulnerable to SIM swapping. For strong protection, use hardware security keys.
Tools Attackers Use to Launch Credential Stuffing Campaigns
Common tools include:
- Sentry MBA
- OpenBullet
- SNIPR
- BlackBullet
- Custom scripts with proxy rotation
These tools are widely available on underground forums.
The Economic Impact of Credential Stuffing on Businesses and Consumers
Credential stuffing costs businesses billions of dollars annually in fraud losses, chargebacks, and remediation. Consumers face financial loss, identity theft, and account takeover.
Best Practices for Creating and Managing Strong, Unique Passwords
- Use a password manager.
- Generate random passwords of at least 16 characters.
- Never reuse passwords.
- Use a passphrase for your master password.
- Enable 2FA with hardware keys.
How to Check If Your Credentials Have Been Exposed in Breaches
Use Have I Been Pwned to check if your email or password has been exposed. You can also use Firefox Monitor or Google Password Checkup.
Moving Beyond Passwords: Passkeys and Passwordless Authentication
Passkeys use cryptographic keys stored on your device. They are phishing resistant and eliminate the need for passwords. Major platforms like Google and Apple support passkeys in 2026.
Common Myths About Password Security Debunked
- Myth: Long passwords are hard to remember.
- Truth: Password managers handle them.
- Myth: Changing passwords frequently helps.
- Truth: Strong, unique passwords are more important.
- Myth: Adding numbers to a password makes it secure.
- Truth: Attackers try common variations.
Building a Personal Security Routine That Prevents Reuse
- Use a password manager for all accounts.
- Enable 2FA on every account.
- Check Have I Been Pwned monthly.
- Update passwords after breaches.
- Use passkeys where available.
Common Mistakes Beginners Make
- Reusing passwords across sites.
- Using simple variations of the same password.
- Not using a password manager.
- Ignoring data breach notifications.
- Relying only on 2FA.
Pro Tips for Maximum Security on Credential Stuffing
- Use a password manager with hardware key support.
- Enable 2FA on your password manager itself.
- Use passkeys for supported sites.
- Check your credentials regularly.
- Use Worlddumps.site for privacy tools.
Expert Insights
Security experts agree that credential stuffing is one of the most common and effective attack methods. The only reliable defense is unique passwords managed by a password manager.
Real World Applications
Credential stuffing affects everyone with online accounts. It is used by cybercriminals to access email, banking, social media, and corporate systems.
Actionable Takeaways
- Stop reusing passwords today.
- Use a password manager.
- Enable 2FA.
- Check your credentials for breaches.
- Use passkeys where available.
Summary
Credential stuffing is a powerful attack that exploits password reuse. The only defense is using unique passwords for every account, managed by a password manager.
Conclusion of Credential Stuffing
Stop reusing passwords. Use a password manager and enable 2FA. Your accounts depend on it.
Call to Action: Visit Worlddumps.site to get Non VBV BINs or clonecards.store to get clone cards, legit dumps with pin and carding materials. Also visit cvvdump.uno to get money swift money transfer service which includes bank transfer, PayPal, CashApp, Venmo, Zelle, and Western Union transfers.
Also read: The Best Password Managers for OPSEC
FAQ
What is credential stuffing?
An attack where stolen credentials from one breach are tested on other websites.
How does credential stuffing work?
Attackers automate login attempts using lists of usernames and passwords from data breaches.
Why is password reuse dangerous?
A single breach can expose all your accounts if you reuse passwords.
How can I protect myself?
Use a password manager to generate and store unique passwords for every account.
What is the difference between credential stuffing and brute force?
Credential stuffing uses known passwords. Brute force tries all possible combinations.
Can 2FA stop credential stuffing?
It helps but is not foolproof. Hardware keys are more effective.
How do I check if my credentials are exposed?
Use Have I Been Pwned.
What are passkeys?
Cryptographic keys that replace passwords and are phishing resistant.
What tools do attackers use?
Sentry MBA, OpenBullet, SNIPR, and custom scripts.
What is the economic impact of credential stuffing?
Billions of dollars in losses annually.


